Fractional CISO
Fractional CISO support for ongoing security leadership.
A chief information security officer (CISO) connects technical risk to organizational decisions. I provide that leadership through a monthly engagement, so you can develop a security program without hiring a full-time CISO.
Who this is for
California small and midsize businesses, water districts, public agencies, and nonprofits that need ongoing security leadership alongside their existing staff and providers.
Consider this engagement when security decisions keep returning to leadership without a consistent owner, priorities are unclear, or policies and incident plans need sustained attention.
What you receive
Policy direction
Security policies connected to the way your organization works, with responsibilities that can be discussed and assigned.
Vendor review
Review of security questions around service providers, their access, and their responsibilities within the agreed scope.
Leadership reporting
A recurring view of security priorities and the decisions that need leadership attention.
Incident planning
Planning for who makes decisions, who communicates, and how the organization coordinates when a security incident occurs.
Illustrated guide
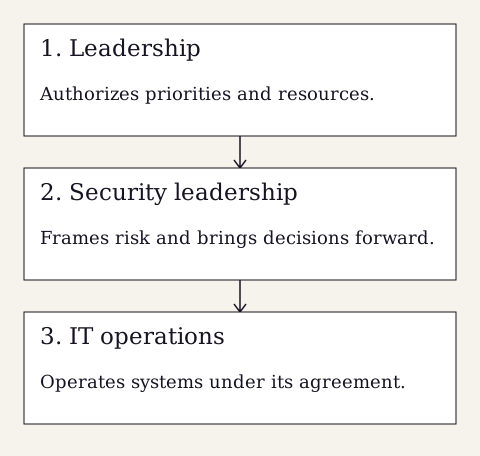
Read the diagram as text
- Leadership: Authorizes priorities and resources.
- Security leadership: Frames risk and brings decisions forward.
- IT operations: Operates systems under its agreement.
How the work happens
- Establish the starting point
Discuss your organization, existing IT support, and the decisions that need a security owner.
- Agree the monthly scope
Define the leadership responsibilities, working cadence, and deliverables for the engagement.
- Keep decisions moving
Review priorities, maintain the agreed program work, and bring decisions to the people who can authorize them.
Agree the scope before the work.
This is a monthly security leadership engagement. It does not imply a staffed security operations center, round-the-clock monitoring, an emergency response hotline, or a replacement for every IT function.
What to bring to the first conversation
- Your current IT support arrangement and leadership structure.
- The policies or reporting requests that need attention.
- Important vendor relationships and known risk questions.
- The decisions that have been delayed because ownership is unclear.
Start with a high-level description. Do not send passwords, access credentials, or sensitive client records.
Book a 20-minute callQuestions, answered
What you may be wondering.
What is a fractional CISO?
A fractional chief information security officer provides security leadership on a defined ongoing basis rather than as a full-time employee. CyberWiz offers monthly policy work, vendor review, leadership reporting, and incident planning.
Is a fractional CISO the same as a managed IT provider?
No. The roles can work together. A managed IT provider often operates systems; a fractional CISO helps define security priorities, responsibilities, and leadership decisions. Exact responsibilities belong in the engagement scope.
Do you provide emergency incident response?
The published engagement includes incident planning. It does not include a promised emergency response service or round-the-clock availability.
Can a nonprofit use a fractional CISO?
Yes. The service is intended for mission-driven nonprofits as well as California public agencies, water districts, and small businesses that need security leadership.
Start with a conversation
What security question is on your desk?
Tell me what prompted the question. A 20-minute call is a place to establish the next step.